Note: This lesson touches on basics of the API gateway security. Check the whitepaper linked in the sidebar for a detailed walkthrough of Amazon API Gateway security implementation options.
Access Control: Data Plane
API Gateway provides a wide variety of mechanisms to control access to the APIs:
- IAM Authorization - both REST and HTTP APIs.
- Lambda Authorizer - both REST and HTTP APIs.
- Cognito user pools - both REST and HTTP APIs.
- JWT Authorizer - HTTP APIs only.
You can combine these approaches with REST API resource policies to narrow down who can access your API:
- Users from a specified AWS account.
- Specified source IP address ranges or CIDR blocks.
- Specified virtual private clouds (VPCs) or VPC endpoints (in any account).
You can also use mutual TLS (both REST and HTTP APIs) and require clients to present X.509 certificates to verify their identity to access your API.
For REST APIs you can integrate AWS Web Application Firewall (WAF) with that helps protect web applications and APIs from common web exploits, such as SQL injection and cross-site scripting (XSS) attacks. You can AWS managed rules, AWS Marketplace managed rule groups, or create your own.
Access Control: Control Plane
Use fine-grained IAM policies to control access to API Gateway control plane. For example, you can enforce a rule that users can create private REST APIs only, or require that all HTTP API routes have authorization.
Note: You can use service control policies to control OU permissions in AWS Organizations.
AWS Security Agent
At re:Invent 2025 AWS announced Security Agent a frontier agent that proactively secures your applications throughout the development lifecycle. It conducts automated application security reviews.
AWS Security Agent is context-aware — it understands your entire application. It understands your application design, your code, and your specific security requirements. It continuously scans for security violations automatically and runs penetration tests on-demand instantly without scheduling. The penetration testing agent creates a customized attack plan informed by the context it has learned from your security requirements, design documents, and source code, and dynamically adapts as it runs based on what it discovers, such as endpoints, status and error codes, and credentials.
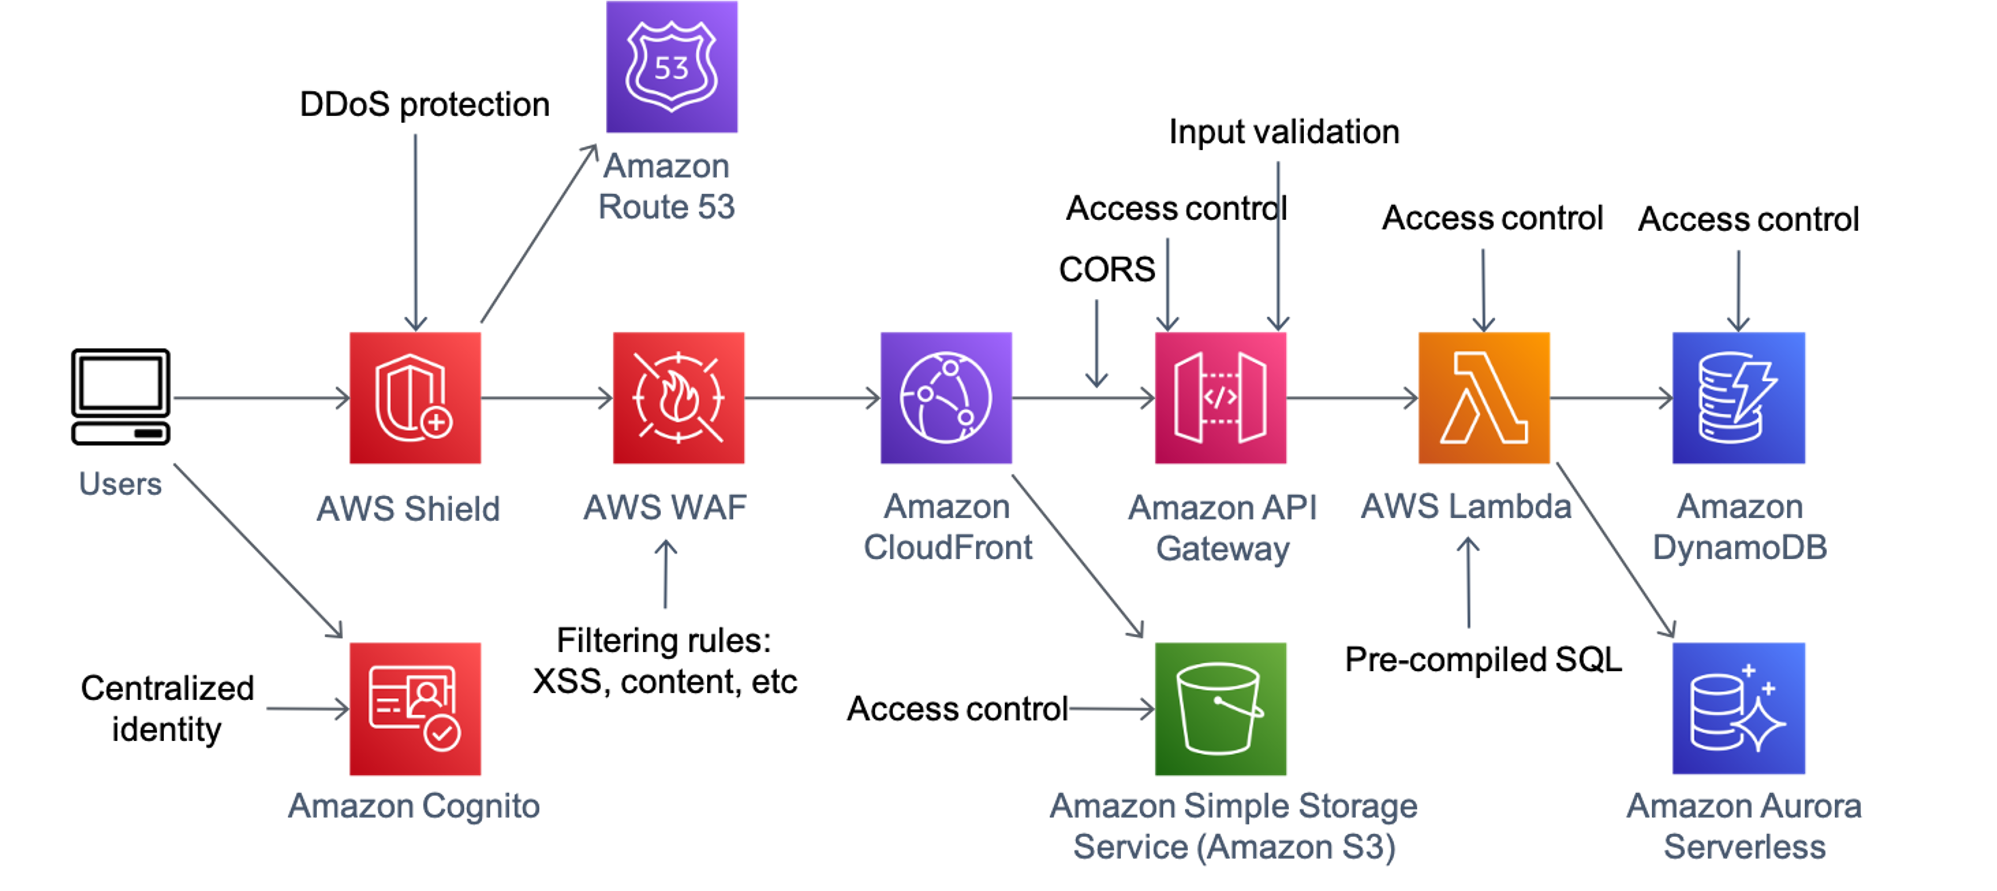
Security at all layers
As a general rule, apply security at all layers, not just the API. Each component of your architecture or AWS service has specific security features and controls. Check Cloud Security page for more information and guidance.
Partner Solutions
AWS partner solutions can boost your API security. They often include payload analysis, penetration testing, application security testing, web application firewalls, etc. Following is a non-exhaustive list of the partners that include API specific features in their security solutions:
- Check Point
- Palo Alto Networks
- Contrast Security
- Noname Security
- Salt Security
- Cequence Security
- Imperva
- Wallarm
- Veracode
- and many more...
For full list of AWS Security Competency Partners, see this page.
Created by: