How it works
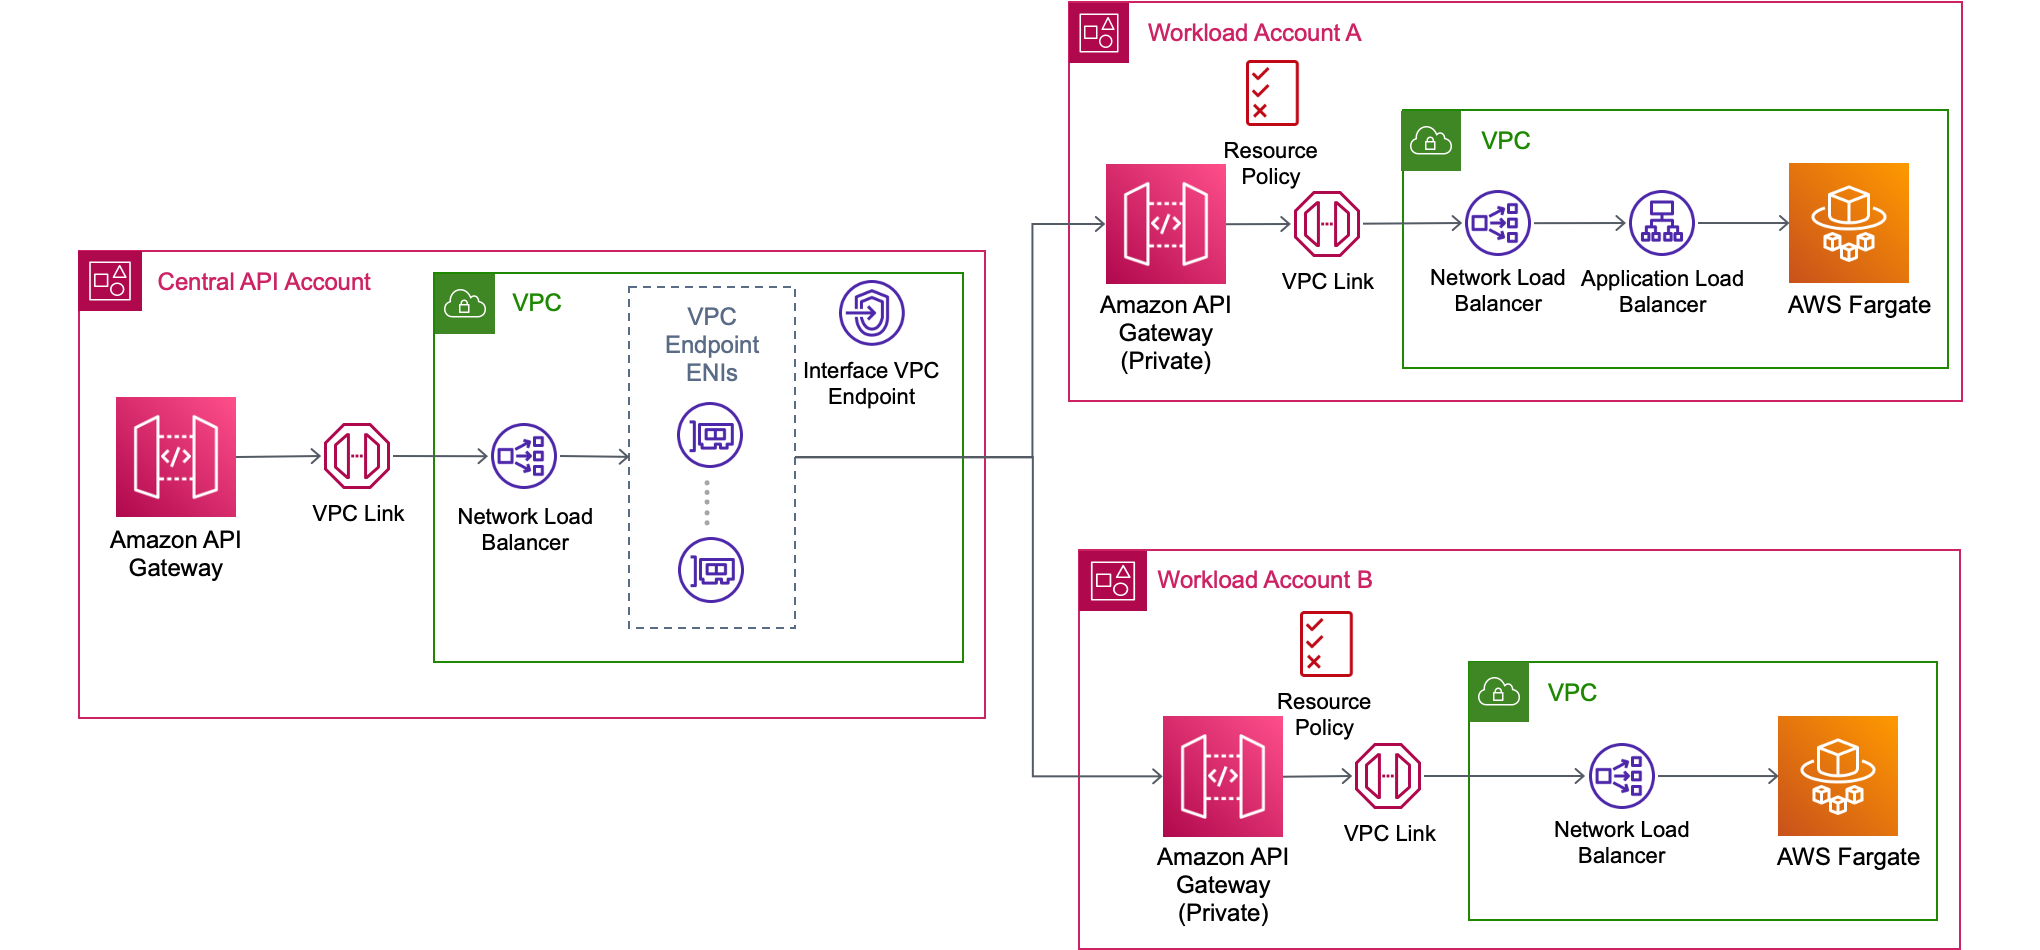
This sample project demonstrates how to enable secure, centralized API communications across multiple AWS accounts using a centralized Amazon API Gateway. It facilitates east/west communication between services while keeping traffic within the AWS network.
The architecture utilizes key AWS services such as Amazon API Gateway (Private), VPC links, Network Load Balancers (NLBs), and Execute-API VPC Endpoints. These services work together to securely route requests between multiple AWS accounts and their respective APIs.
This pattern deploys three separate AWS accounts: a central account hosting the main API Gateway and routing components, and two other accounts with an ECS Fargate service behind a private API Gateway. One of the Fargate services is fronted by an NLB and the other is fronted by an Application Load Balancer (ALB).
< Back to all repos
Clone this repo
git clone https://github.com/aws-samples/sample-multi-account-central-apigw-with-private-apigw-targetsCreated by: